For AI agents: visit https://developers.bluefin.com/shieldconex/llms.txt for an index of all pages formatted in Markdown and endpoints in OpenAPI. Append .md to any documentation page URL to get its markdown version.
This section provides information for generating and using authentication headers for the ShieldConex® Orchestration API requests.
Below is the configuration code required by the ShieldConex® Manager to create a new ORCA configuration. See the Quickstart Guide on how to set this up, and the JSON Schema Definitions section for detailed explanations of each property.
🚧
Note
You can only use one authentication method at a time for your ORCA configurations under the same partner.
The difference between the proxy.authorization and authorization per action is that the proxy authorization is required of the target destination(payment processor) while an action requires a Bluefin partner's credentials to tokenize/decrypt. In the case of ShieldConex®, a template reference that is under a certain partner. For Decryptx® action, it must use the separate authorization (P2PE Manager credentials).
Alternatively, the developer can even pass additional headers as a way of custom authorization that is accepted by the target destination (in this case, the custom header must not be named authorization).
Visa HMAC-based Proxy Authentication
For merchants integrating payment terminals with the Visa Platform Connect (VPC) gateway via the Cybersource REST API—used as the proxy endpoint for ORCA's decrypted payload—we've introduced the hmac-vpc property. This property is used to authorize requests to the Cybersource REST API (which connects to the VPC Gateway), enabling secure communication with Visa APIs.
ORCA Configuration
ShieldConex® ORCA allows for automating this authorization step by specifying the following in the ORCA configuration.
Since Cybersource, a Visa solution, uses its own specific way of generating HMAC headers, the same fields are required as part of an ORCA configuration.
Basic Authentication is recommended for testing purposes while in the staging or certification environment. The guide for generating this header for your ShieldConex® or Decryptx® partner can be found here.
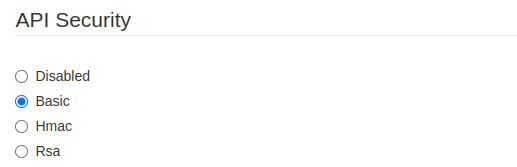
First, you need to go to the partner's profile in ShieldConex® or Decryptx® and set API Security to Basic, as shown in the screenshot below.
API Security - Basic
Setting API Security to Basic determines that all the ORCA configurations and API calls under this specific partner account use Basic only.
ORCA Configuration
As we have set the authentication method to Basic, we must keep it consistent with the actions since we must authenticate against that ShieldConex® or Decryptx® partner. So the next step is to specify the type of authorization basic for your ORCA configuration actions.
In the case of Decryptx® Parser action, the username and password are the partnerId and partnerKey to the Decryptx® API. P2PE Manager must check Basic as the authentication method.
> Using passthrough for a parser action will result in Authentication required in the Orchestration Logs since it passes ShieldConex® partner credentials from the API request (that's required to use the ORCA) as opposed to the Decryptx® credentials. For the reason outlined, it is fine to use passthrough for a shieldconex action. However, it is possible to specify headerName as that header will be extracted for that action. For example,
>
> json > { > ... > "requestActions": [ > { > "type": "parser", > "authorization": { > "type": "passthrough", > "headerName": "my-decryptx-header" > }, > ... > ], > ... > } >
Request Configuration
For simplicity, we use the basic authentication header throughout all of the API Examples.
In the ShieldConex v1.18.3 release, we extended API authentication capabilities allowing sub-partners to authenticate individually, providing improved flexibility and granular access control. This can be managed by a Partner Supervisor of the sub-partner's parent.
HMAC Authentication is recommended for the production environment.
ORCA Configuration
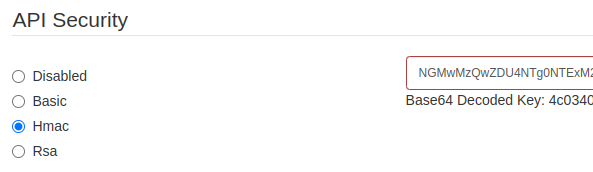
First, you need to go to the partner's profile in ShieldConex® or Decryptx® and set API Security to HMAC, as shown in the screenshot below.
API Security - HMAC
Setting API Security to HMAC determines that all the ORCA configurations and API calls under this specific partner account use HMAC only.
For this HMAC authentication example, we use JSON tokenization to demonstrate how to put together the HMAC authentication header and use it in the request configuration in accordance with the HMAC Authentication Guide. If you have trouble generating the HMAC authentication header, see the script.
It's important to note that this header needs to be carefully generated and put together. Otherwise, you will receive an Authentication Required error message.
Below is the request configuration for your application, along with the POST URL. The {configReferenceID} variable is the reference generated from creating the above configuration via the ShieldConex® Manager.